Policies
Policies configure Windows settings on your managed devices and show whether each device complies with the configuration you want.
In short
- Policies starts off in a new tenant. An Admin or Owner turns it on; leave it off if Microsoft Intune, Group Policy or another tool already manages Windows settings on your devices.
- Start from the Library of recommended baselines, or build your own policy from the settings catalog.
- Nothing you change on a policy's page takes effect until you click Save Changes.
- Assign a policy to device groups; devices pick it up at their next check-in, and devices in excluded groups are skipped.
- When settings conflict, the policy with the higher priority number wins.
- Windows Update is not configured here; SmartPatch does that on the Windows Update page.
Turn Policies on or off
A new tenant starts with Policies off, and the Policies page explains what it does instead of showing the library. Only Owners and Admins can turn it on.
Warning
Open Policies in the sidebar.
Click Turn on Policies, then confirm.
The library and your policy tabs appear.
To turn it off again, delete the tenant's policies first; Turn off Policies then appears at the top of the page.
The Policies page
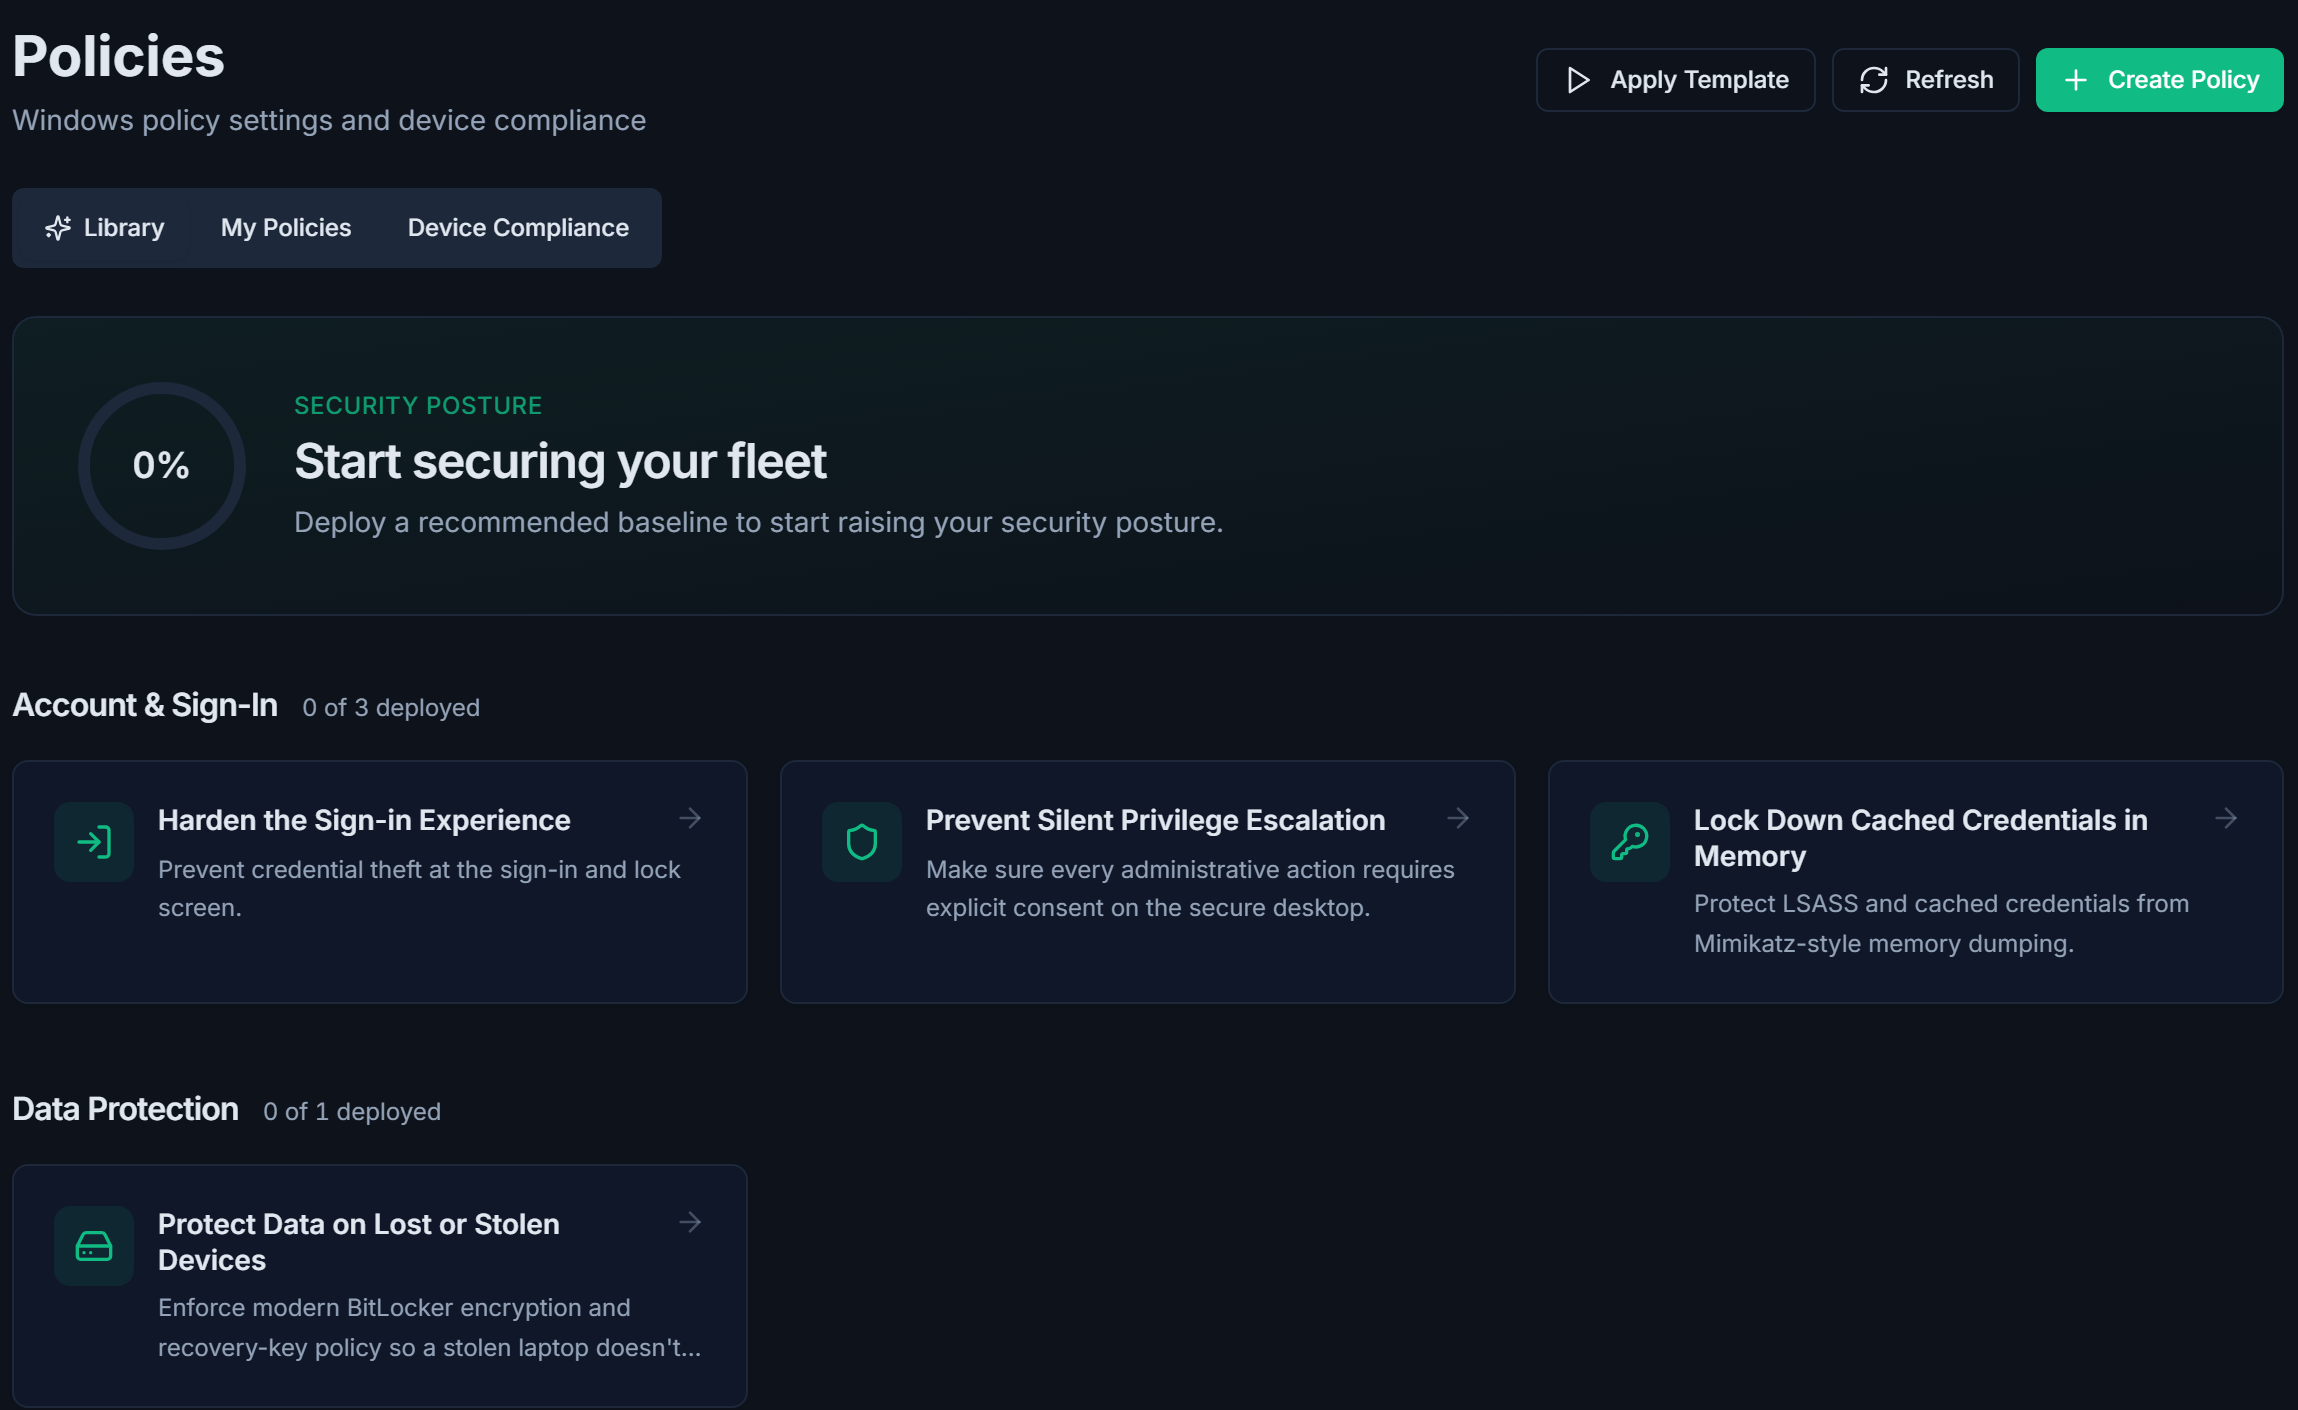
The Policies page has three tabs:
- Library
- Recommended baselines you can deploy in a few clicks.
- My Policies
- Manage your own policy profiles.
- Device Compliance
- See which devices are compliant with their assigned policies.
The page opens on Library until your tenant has at least one policy, and on My Policies after that. On the My Policies and Device Compliance tabs, four summary cards sit at the top:
- Total Policies
- Number of policy profiles created, with the enabled count.
- Devices with Policies
- How many devices have policies assigned.
- Compliant Devices
- Devices that meet all of their assigned policies.
- Non-Compliant Devices
- Devices with at least one policy they do not meet.
Deploy a baseline from the Library
The Library tab lists recommended baselines grouped by category, with a summary of how many you have deployed so far. Click a baseline to see the settings it changes, why it matters and what users will notice.
Keep or change the Policy name.
Optionally choose a group under Assign to group.
Or leave it on No assignment and assign it later.Click Deploy baseline.
A baseline you have already deployed offers Deploy as new instead.
The deployed baseline becomes an ordinary policy on the My Policies tab, where you can change its settings and assignments like any other.
Create a policy
Go to Policies in the sidebar.
Click Create Policy.
Enter a name.
For example "Security Baseline" or "Kiosk Lockdown".Optionally add a description.
Click Create Policy.
You're taken to the policy detail page to add settings.
Add settings to a policy
Settings come from a comprehensive catalog covering Windows configuration areas like security, networking, user experience, and more.
Click Add Setting on the policy detail page.
Browse the settings catalog by category and subcategory, or search for a setting by name.
Select a setting, enter the value you want, and click Add.
It appears under Pending Settings (not saved yet).Repeat for each setting you want to include.
Click Save Changes at the top of the page.
Nothing you add or change on this page (settings, values, name, description, Enabled or Priority) takes effect until you click Save Changes. Removing a saved setting with its delete button takes effect straight away, after you confirm.
Note
Policy properties
These are in the Policy Details card on the policy's page:
- Name
- Descriptive name for the policy.
- Description
- Optional notes about the policy’s purpose.
- Enabled
- Whether the policy is actively enforced.
- PriorityHigher number = higher priority
- Decides which policy takes precedence when settings conflict.
Assign a policy to groups
Open a policy’s detail page.
In the Assignments card, click Assign.
Select the target device group.
Optionally tick groups to leave out under Exclude groups.
A device in an excluded group is skipped even when it is also in the target group.Click Assign.
All devices in the group, except those in an excluded group, receive the policy settings on their next check-in.
Change exclusions or remove an assignment
Click Exclusions next to the group assignment to change which groups it leaves out. Devices that become excluded stop receiving the policy on their next check-in and the agent reverts its settings; devices that stop being excluded pick it up the same way. The All Devices group cannot be excluded.
To remove a policy from a group, click the remove button next to the group assignment.
Policy templates
If you work across your whole account (the Account Owner, or an MSP Technician with access to all tenants), you can reuse policies between tenants. MSP Read Only users see these buttons greyed out.
- Save as template
- The copy icon on a policy row saves that policy and its settings as a reusable template.
- Apply Template
- The button at the top of the page adds a template’s policies to the current tenant. Policies that already exist are skipped.
In a tenant with Policies off, applying a template skips its policies and says so. Group assignments are not part of a template. See Templates for capturing and applying templates across many tenants at once.
Monitor compliance
My Policies tab
Each policy row shows:
- A compliance icon indicating status
- Whether the policy is enabled or disabled
- Number of configured settings and assigned groups
- Priority level
- Last updated date
Open a policy to see its Compliance Status card, which lists each assigned device's state for that policy. A device shows Superseded there when every setting it does not meet is overridden by a higher-priority policy, so the device is correctly configured. A device shows Error for a policy whose settings are all per-user ones, because Pckgr applies machine-wide settings only.
Device Compliance tab
This tab shows per-device compliance status. The status counts the device's assigned policies:
| Status | Meaning |
|---|---|
| Compliant | The device meets every assigned policy. A policy that is superseded by a higher-priority one counts as met. |
| Non-Compliant | The device meets none of its assigned policies. |
| Partial | The device meets some but not all of its assigned policies, and shows how many, for example “Partial (3/5)” for 3 of 5. |
| No policies | The device has no policies assigned. |
The table also shows each device's hostname, how many of its policies (and settings) it meets, its OS version and its last check-in. Click any device to view its full details, including specific compliance information.
Delete a policy
Click the trash icon on a policy row and confirm. If the policy is assigned to groups, a warning shows how many groups will be affected.
Tips
- Start with a small pilot group to test policy settings before rolling them out broadly.
- Use the priority field to control which settings win when multiple policies target the same device.
- Check the Device Compliance tab regularly to identify devices that have drifted from your desired configuration.
- Use the search bar to quickly find specific policies or devices.
- Windows Update settings are managed by SmartPatch on the Windows Update page, not with policies.